Information Security Review
PROSee your ISO 27001 gaps and what to fix first.
Assess an organisation's information security management against a recognised standard — primarily ISO/IEC 27001 (ISMS) — producing a control-domain gap assessment with maturity and prioritised actions, grounded in the current standard and cited, never reproducing licensed clause or Annex text. Use when asked for an information security review, ISO 27001 gap analysis, or ISMS assessment.
Ask for it in plain English, e.g.
Works in
You ask: Northwind SaaS (a fictional startup) wants to know how far it is from ISO/IEC 27001. It has cloud infrastructure, a small team, and no formal security program yet. Run an information security review and show the gaps.
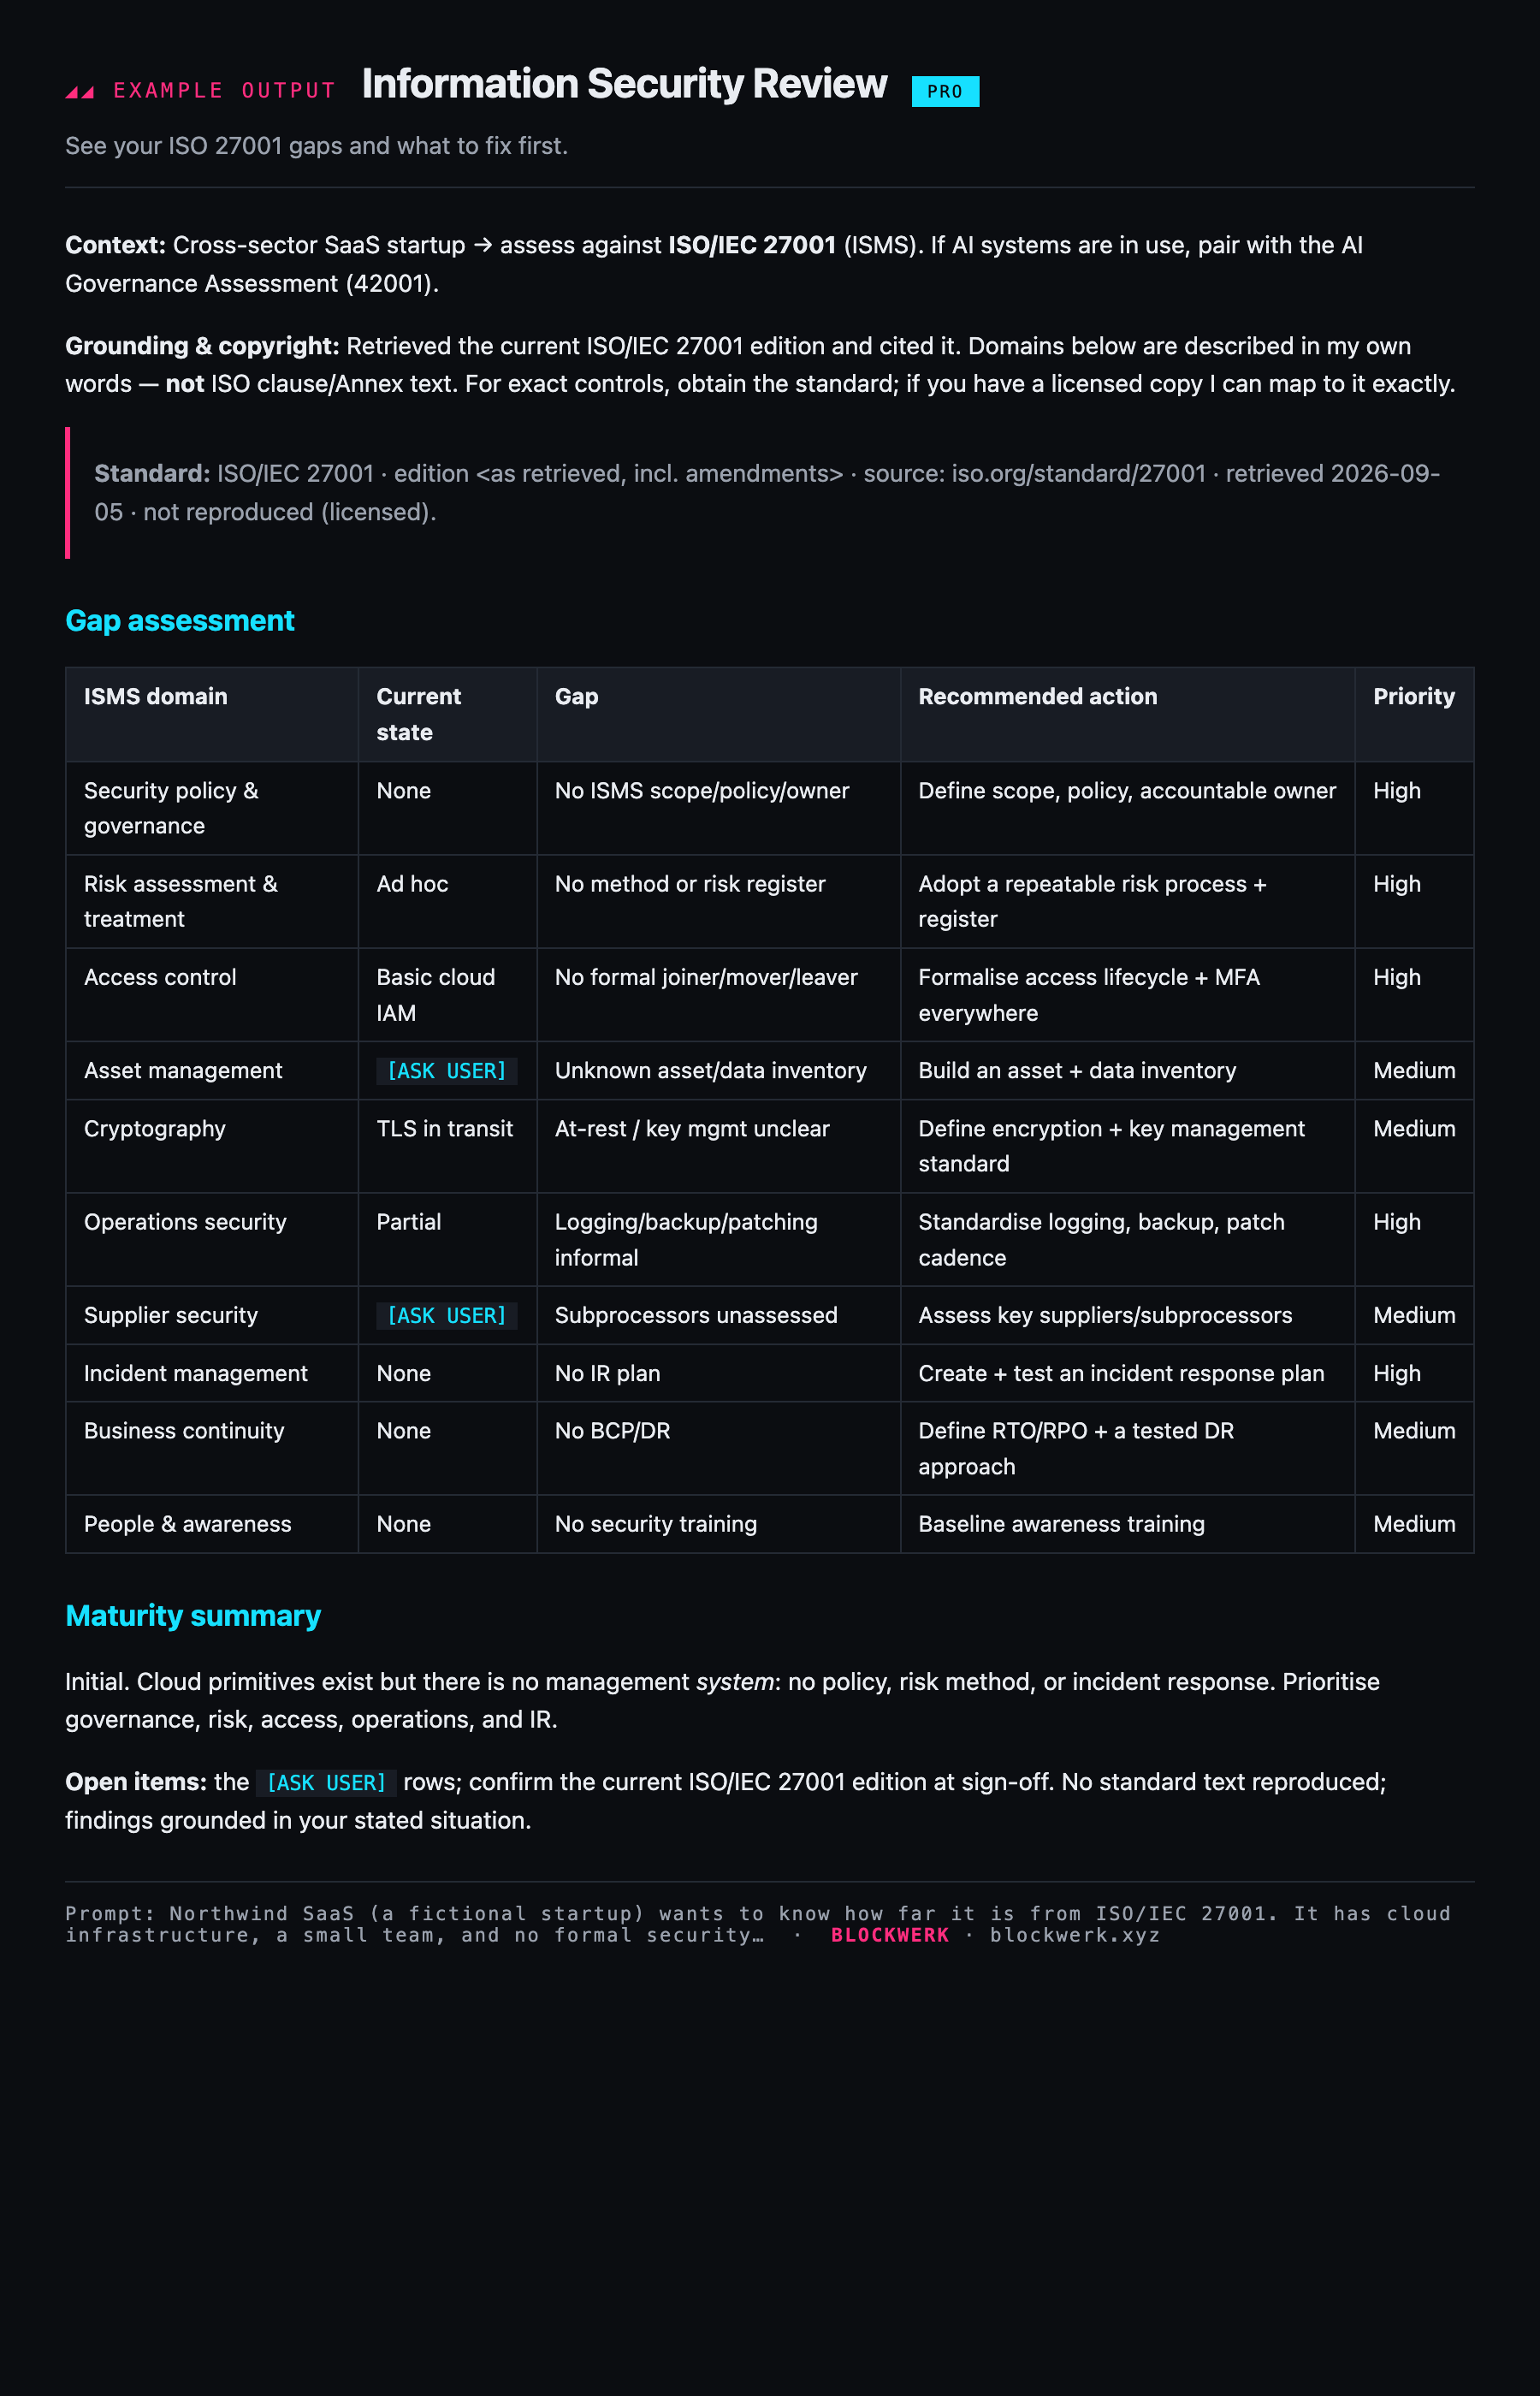
Example output shown for illustration. Your assistant produces this live from your own request once the skill is installed.